HIPAA Compliance & Data Security
At CaliMed Billing, the security of your practice's financial data and the privacy of your patients' Protected Health Information (PHI) are the foundations of our service. Operating in the Golden State requires adherence to some of the nation's most rigorous privacy standards. We maintain a strictly HIPAA-compliant framework, ensuring that every stage of your Revenue Cycle Management (RCM) meets both federal and state-level security mandates.
Our Multi-Layered Security Approach
We implement advanced technical and administrative safeguards to protect your practice from data breaches and regulatory penalties:
End-to-End Encryption
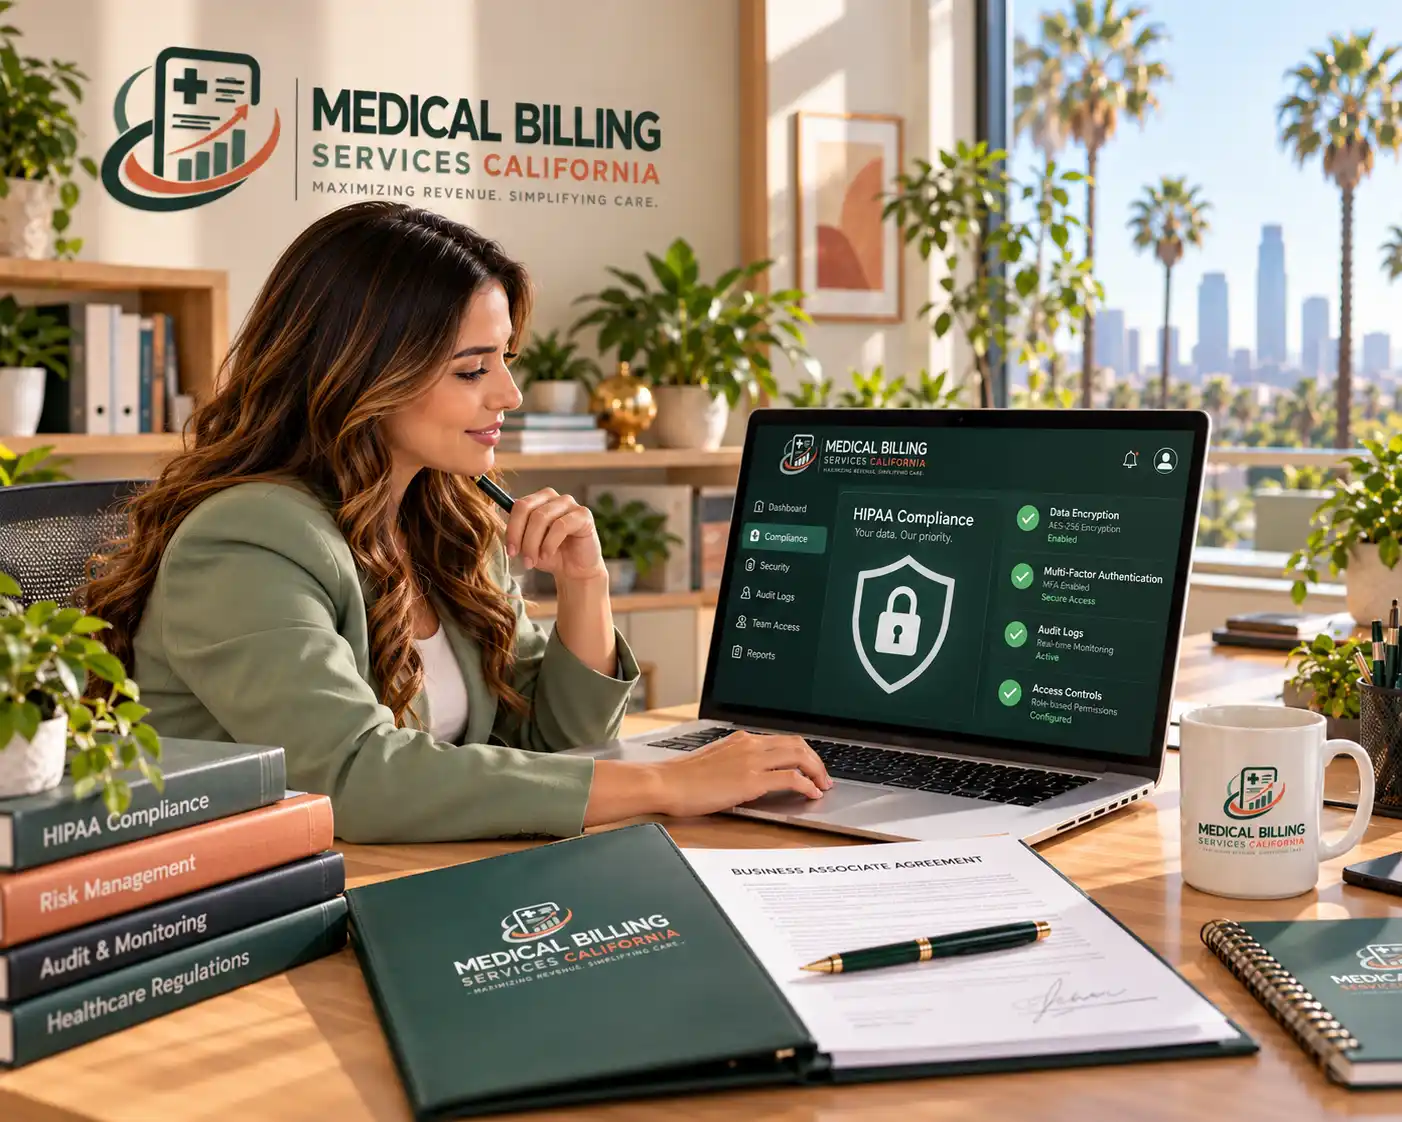
All data transmitted between your California practice and our secure systems is protected using industry-standard 256-bit encryption.
Multi-Factor Authentication (MFA)
We utilize MFA and role-based access controls to ensure that only authorized personnel can interact with sensitive records.
Secure EHR/EMR Integration
Our team maintains Secure EHR Access to your existing platforms, such as Epic, Cerner, or athenahealth, without storing data on local remote devices.
Business Associate Agreements (BAA)
We execute formal BAAs with every client, legally binding our team to uphold all HIPAA and HITECH Act requirements.
Compliance in the California Landscape
California healthcare providers face unique oversight from the California Department of Health Care Services and specific state privacy laws. Our compliance protocols are designed to address these localized requirements:

Audit-Ready Documentation
We maintain detailed audit trails and activity logs for all billing transactions. This ensures that if your practice is subject to a CMS or payer audit, you have a transparent, compliant record of all medical billing and coding activities.
Continuous Staff Training
Every member of the CaliMed Billing team undergoes regular, rigorous HIPAA and data ethics training. This ensures our staff is always updated on the latest federal and California-specific privacy regulations.
Secure Payer Coordination
When managing claims with Medi-Cal, Blue Shield of California, or Kaiser Permanente, we use secure Electronic Data Interchange (EDI) channels to prevent data exposure during transit.
Why Security is a Priority for California Doctors
Mitigate Liability
Professional, compliant billing reduces the risk of costly data breaches and state-level regulatory fines.
Protect Patient Trust
Demonstrating a commitment to the highest security standards enhances your practice’s reputation in your local community.
Defend Against Audits
Our proactive compliance monitoring identifies potential risks before they become legal or financial liabilities.
FAQ’s
Yes. We use encrypted systems and US-based infrastructure to comply with all federal HIPAA and HITECH standards.
We maintain strict internal protocols and incident response plans that align with federal and California state notification requirements.
Absolutely. We provide a signed Business Associate Agreement to every practice as part of our standard onboarding process.