Maximizing revenue. Simplifying care.
Home/Privacy Policy

Privacy Policy

At CaliMed Billing (medicalbillingservicescalifornia.us), we are committed to maintaining the highest standards of data security and patient confidentiality. Operating in California requires compliance with an integrated framework of federal and state laws, including HIPAA, the Confidentiality of Medical Information Act (CMIA), and the California Consumer Privacy Act (CCPA/CPRA). We ensure that every stage of your Revenue Cycle Management (RCM) process meets these rigorous mandates.

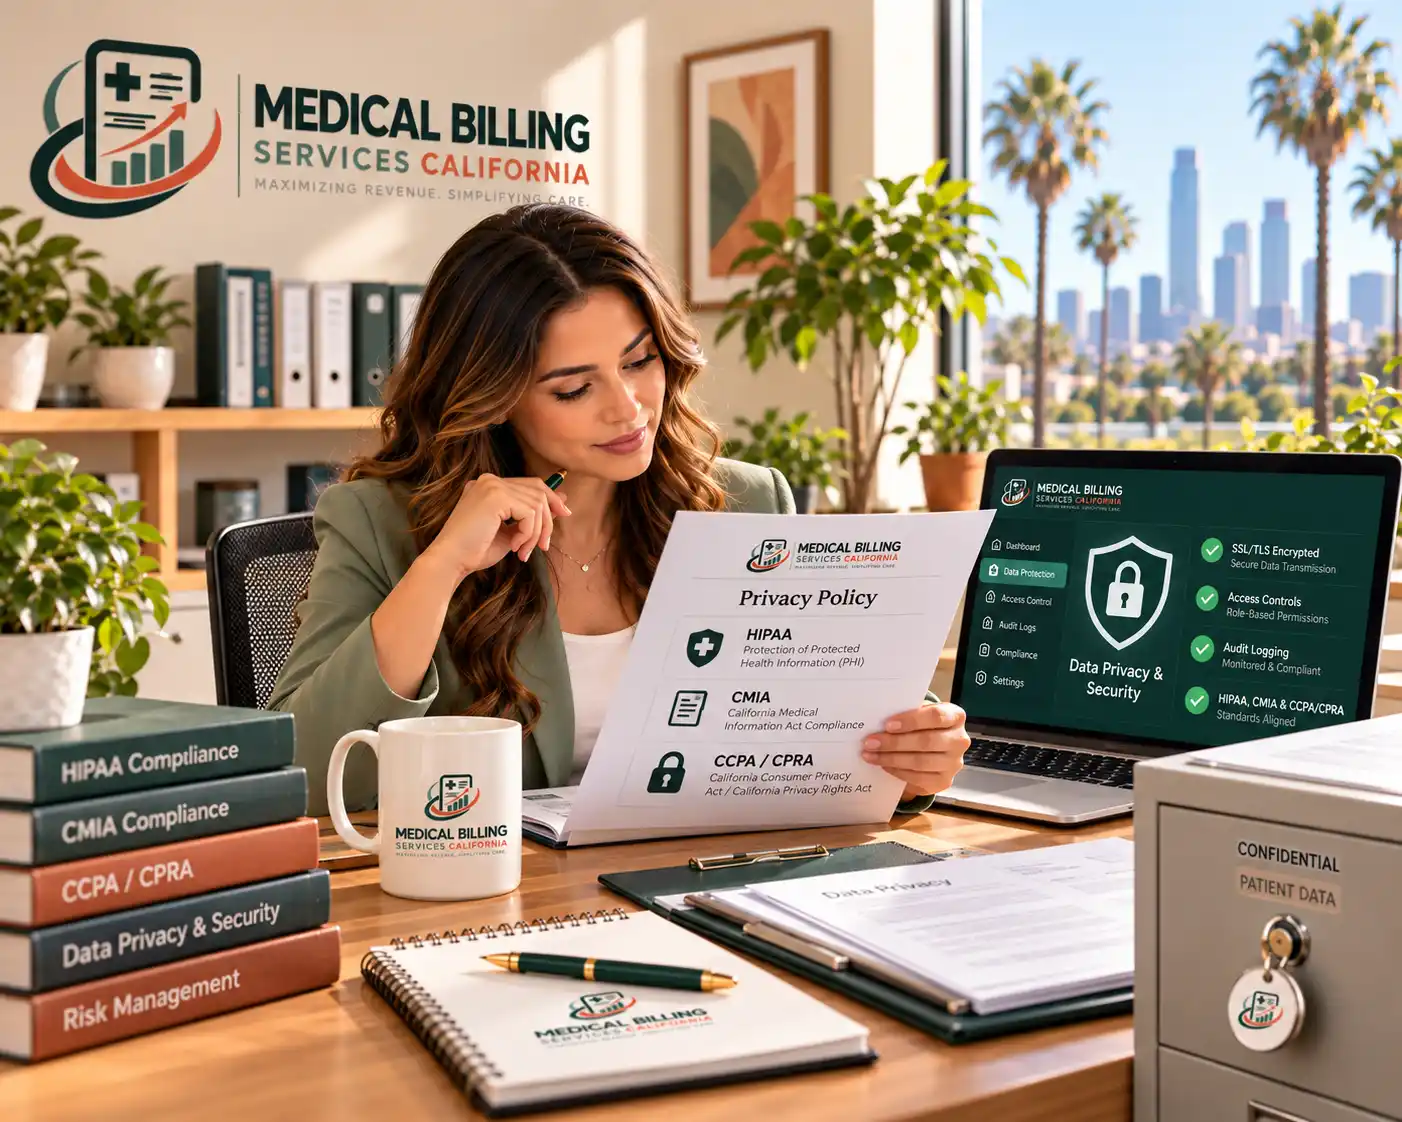
CaliMed privacy specialist reviewing a HIPAA, CMIA and CCPA/CPRA privacy policy beside a data protection dashboard

1. Information We Collect

In order to provide comprehensive medical billing and coding services, we collect various categories of information:

Personal Identifiers: Name, practice address, email address, and phone number provided voluntarily through our site.

Protected Health Information (PHI): Patient medical records, treatment details, and insurance identifiers required for billing.

Technical Data: Automatically logged information such as IP addresses, browser types, and domain names used to monitor site performance.

Practice Information: Specialty type, practice size, and billing volume to tailor our RCM solutions.

2. How We Use and Protect Data

We utilize collected data strictly for professional billing and operational purposes:

Managing RCM: Processing transactions, submitting claims, and managing denial follow-ups.

Communication: Responding to inquiries and sending transactional or relationship-based updates.

Compliance: Meeting legal and regulatory standards set by CMS and the California Department of Health Care Services.

Site Improvement: Analyzing usage statistics to enhance the quality and security of our online platform.

3. Data Protection and Security Measures

CaliMed Billing implements multi-layered safeguards to prevent unauthorized access or disclosure of sensitive data:

End-to-End Encryption: We utilize SSL/TLS protocols to encrypt ePHI both at rest and during transmission.

Secure Access Controls: Implementation of strong authentication and role-based permissions ensures only authorized personnel access PHI.

Zero-Downtime EHR Integration: We maintain Secure EHR Access to your existing platforms (e.g., Epic, Cerner) without storing data on unencrypted local devices.

Physical Safeguards: Locked filing areas and restricted access zones to protect all physical records.

4. California Privacy Rights

California residents and providers benefit from additional state-level protections:

CCPA/CPRA Rights: You have the right to know what personal information is collected, request its deletion, and opt out of its sale or sharing.

CMIA Compliance: We adhere to the Confidentiality of Medical Information Act, which requires stricter authorization processes and audit trails than federal law in some cases.

Patient Access (PAHRA): We support the shorter timelines required under California law for responding to patient access requests.

Breach Notification: In the event of an unsecured PHI breach, affected individuals will be notified within 60 days of discovery as mandated by both federal and state law.

5. FAQ’s

We use 256-bit encryption, multi-factor authentication, and secure VPNs to ensure data is never compromised during remote processing.

No. We do not sell, rent, or lease customer lists or personal information to third parties.

Yes. Every billing specialist undergoes rigorous training on HIPAA, CMIA, and CCPA to ensure total compliance with Golden State regulations.